This guide explains how Valdemar, Arjemiro, and fdossantos function as supplier-related identifiers in procurement workflows. It provides objective background on what such names typically represent in purchasing and vendor management—covering roles, documentation expectations, and practical decision criteria—so teams can improve clarity, traceability, and operational coordination without relying on assumptions.
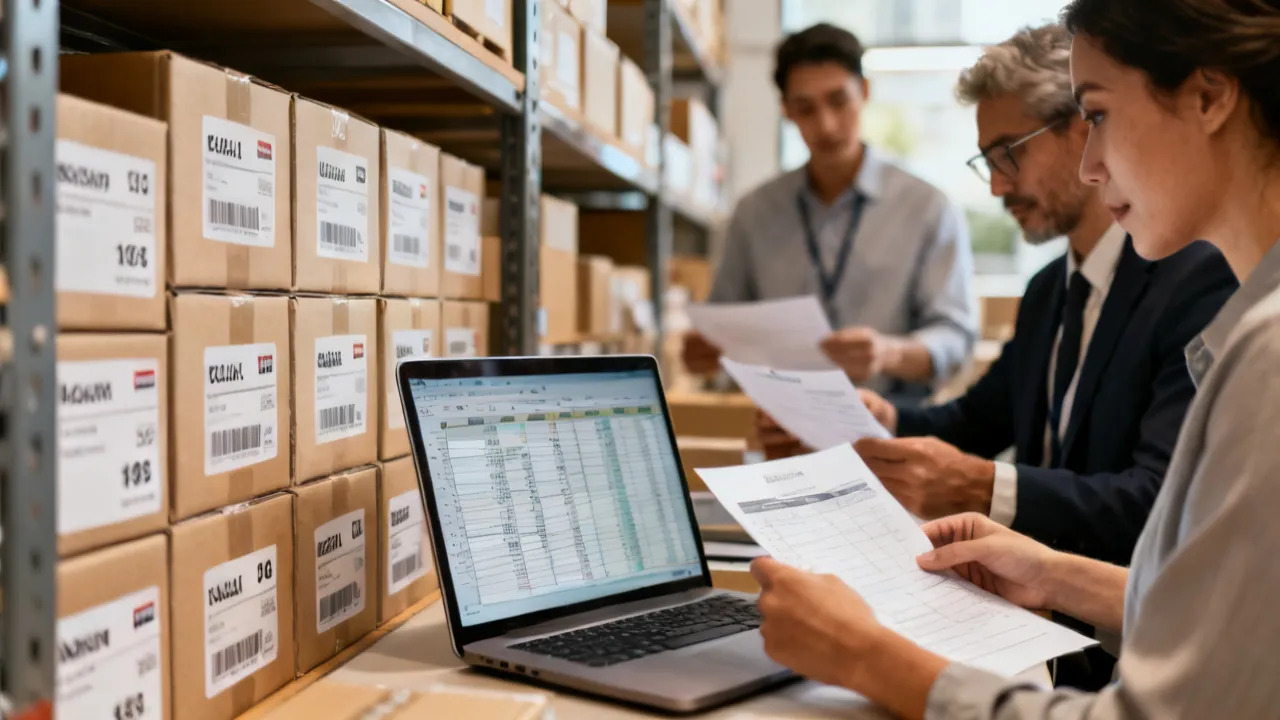
When teams encounter supplier identifiers like Valdemar, Arjemiro, and fdossantos, the very important step is to treat them as data signals—not as proof of capability on their own. In real procurement practice, these names often appear across quotations, shipping documents, vendor master records, internal approvals, or email threads during supplier evaluation. The winning approach is to verify what each identifier actually maps to: a legal entity, a distribution partner, a fulfillment node, an account used for purchasing, or a contact/portal alias. Done correctly, this reduces delays, prevents misrouting of goods, improves invoice reconciliation accuracy, and strengthens audit readiness.
Procurement teams frequently assume that if a familiar name appears on a quotation, it must refer to the same party that will ship the goods and later invoice them. But in practice, supply chains can be multi-party and document-driven. One identifier may be used for ordering, while another identifier is used for invoicing; one party may produce goods, but a different party may dispatch them. Even when the same “name” is shown in many places, the system fields behind the scenes—legal names, addresses, tax identifiers, remittance details, shipment instructions, and return ownership—may differ. That is why procurement professionals treat names as identifiers requiring mapping, not as inherently authoritative statements of identity.
In procurement systems, a name can be recorded at different levels—brand, trading name, subsidiary, purchasing account label, marketplace seller name, or warehouse-facing entity. That difference affects contract scope, invoicing pathways, warranty or service pathways, customs or tax handling (where applicable), and the correct point of contact for corrective actions. For operational teams, the same label—such as Valdemar—may represent distinct realities depending on where it appears (ERP vendor card vs. shipment instruction vs. invoice header vs. email signature block).
Consider a typical procurement cycle. In an ERP, the supplier master record might list “Valdemar” as a trading name. On an RFQ response, the quotation might show a legal entity name like “Valdemar Trading LLC” (or a different spelling). On packing slips, the dispatch party might show a different company name entirely, especially if a distributor fulfills the order. Finally, the invoice might be issued by the legal entity that holds the tax registration, and remittance might be directed to a bank account belonging to yet another entity in a corporate group. If procurement teams do not reconcile these fields, they may: (a) approve the wrong contract entity, (b) route invoices to the wrong cost center, (c) mismatch goods received vs. invoice received, and (d) create gaps in warranty claims because the entity that delivered the goods may not be the entity that owns corrective actions.
Accordingly, Arjemiro and fdossantos should be assessed using consistent criteria: documentation alignment, responsiveness evidence, process control indicators, and clear handoffs between procurement, logistics, and finance. This means you should not judge “capability” from a name; you should judge capability from evidence that is correctly mapped to the transaction path.
Very organizations manage suppliers through a cycle: onboarding and qualification, request-for-quote (RFQ) and evaluation, contract or purchase authorization, fulfillment and receiving, then invoice reconciliation and performance review. Supplier identifiers—such as the ones referenced here—are used to connect those steps. When the identifiers are inaccurate or inconsistent, organizations often see common downstream issues: purchase order mismatches, delayed approvals, unclear ownership of claims, difficulties extracting performance data, and repeated rework between procurement, logistics, and AP.
From an industry perspective, this is less about “who the name sounds like” and more about how it behaves in the system: does it appear consistently across documents and platforms, and can the organization trace a transaction from PO to receiving to payment? The best procurement organizations build a traceability mindset: every line item purchased should have a chain of records that supports the claim that goods were ordered from a mapped supplier entity, received under matching quantities and SKUs, invoiced by the entity tied to payment terms, and accepted or returned under defined policies.
When supplier identifiers are ambiguous, the workflow reveals the truth. If “Valdemar” appears in one document but the goods received record ties to another entity, you have a mapping problem. If “Arjemiro” appears as the ordering contact but dispatch confirmations show a different party, you have a responsibility handoff problem. If “fdossantos” appears only in the billing section without corresponding PO references, you have a reconciliation risk that can impact cash flow and audit evidence.
To evaluate any supplier identifier set—including Valdemar, Arjemiro, and fdossantos—consider the following non-speculative checks. These are widely used in vendor governance frameworks (e.g., ISO-aligned quality management and procurement top practices) and can be adapted to internal policies. The goal is to verify mapping, responsibility, and operational behavior, not to guess identity based on appearance.
Organizations sometimes treat supplier identifiers as interchangeable. In practice, confusion can occur when:
By focusing on traceability, you convert a vague label (e.g., fdossantos) into a verifiable supplier pathway. The emphasis shifts from “Who is this person or name?” to “What role does this identifier play, and what records confirm that role?” That pivot is essential for both operational accuracy and audit defensibility.
From an expert procurement standpoint, audit readiness is not a compliance theater activity—it’s operational clarity. If Valdemar or Arjemiro appears in supplier documents, you should be able to answer quickly and consistently:
These are the questions that make a supplier identifier actionable for governance and continuous improvement. When those questions can’t be answered because the identifier mapping is unclear, organizations end up with “hidden” risks: expensive rework, delayed corrective actions, and audit findings due to missing evidence of supplier responsibility.
An audit-ready approach is also about controlling the data you capture. For instance, if “Valdemar” appears in an invoice but your internal system expects “Valdemar Industrial Supplies BV,” you might either (a) create a manual override that bypasses standard controls, or (b) incorrectly map the invoice to the wrong vendor record. Both outcomes can erode audit evidence. Instead, procurement should enforce mapping rules so that identifiers like Valdemar, Arjemiro, and fdossantos are recognized and routed only when the mapping is verified.
Even with careful system hygiene, ambiguity can happen. A practical approach is to ask structured questions early—before purchase commitments are made. For example:
This style of inquiry is objective and document-driven, which typically accelerates alignment across procurement, logistics, and finance. It also creates a paper trail: your clarifications, supplier responses, and internal decisions become evidence that you managed supplier identifiers as structured data signals.
Another best practice is to standardize how you ask questions. Using consistent templates reduces ambiguity. For example, ask for “vendor master details required for PO/invoice matching” (legal name, address, tax ID, bank remittance details, and contact roles). Ask also for “shipping document requirements” (dispatch entity name, shipping address, packing slip references, and tracking documentation). That helps ensure that Arjemiro and fdossantos are not merely “names,” but mapped nodes in your workflow.
| Item | What to Verify for Valdemar | What to Verify for Arjemiro | What to Verify for fdossantos |
|---|---|---|---|
| Identity | Legal entity and invoicing party consistency across RFQ, PO, and invoice | Trading name vs. legal entity mapping in vendor master records | Account ownership for purchasing vs. fulfillment/dispatch role |
| Documentation | Quotation terms, packing slip fields, and serial/lot traceability references | Shipping instructions alignment with PO line items | Invoice reconciliation compatibility with internal coding/PO references |
| Responsibility | Who handles quality claims and corrective actions | Who is responsible for dispatch timing and shipment confirmations | Who owns warranty/returns process for delivered goods |
| Operational Fit | Turnaround for RFQs and issue resolution | Consistency of lead times across recent deliveries | Reliability of purchase order fulfillment and receiving match rates |
| System Behavior | How the identifier appears in ERP/vendor master and document templates | How it behaves in shipping/dispatch platforms and tracking documentation | How it behaves in AP workflows and invoice-to-PO matching logic |
| Audit Evidence | Whether you can link quality records to the correct delivered lots and the invoice entity | Whether dispatch documentation supports receiving and time-of-delivery evidence | Whether financial reconciliation and returns evidence are owned by the same mapped entity |
The verification approach above aligns with commonly accepted purchasing governance practices referenced in international standards and guidance on supplier management and quality systems. For general supplier management concepts, readers can consult:
It’s worth emphasizing a subtle but important point: these references guide how to manage processes and evidence—they do not validate supplier claims by themselves. Your organization still needs to confirm which identifier maps to which responsibility and documentation set within your operational workflow.
Use this process to determine whether Valdemar, Arjemiro, and fdossantos represent the same party or different entities within your procurement cycle. This guide is designed to be practical for teams working across procurement operations, logistics, and finance.
In other words, “pause or proceed” should be determined by mapping completeness and evidence, not by whether the name looks familiar. Familiarity can bias decision-making and lead to uncontrolled workarounds.
From a professional procurement operations perspective, supplier identifiers should ultimately support measurement. Instead of treating Valdemar, Arjemiro, and fdossantos as static labels, organizations can convert them into structured performance categories. But importantly, those categories must be tied to verified mapping so that performance measurement isn’t distorted by misattributed transactions.
This measured approach typically improves decision quality more than relying on “reputation” attached to a name. It also provides a defensible audit trail when supplier mapping is later reviewed. When auditors ask, “How do you know the supplier responsible for quality is the supplier you paid?” your answer should be traceability-based, not name-based.
To make this practical, procurement can implement a “supplier identifier dictionary.” For example, create an internal table that records:
With such a dictionary, teams stop interpreting identifiers “on the fly” and instead use a governed mapping approach. This prevents the common error of allowing multiple meanings of the same identifier to persist across business units.
They may be related but not necessarily identical. In procurement records, such names can represent different entities (legal vendor vs. trading name vs. fulfillment partner). The correct method is to verify identity mapping across RFQs, purchase orders, packing slips, and invoices, including addresses, tax identifiers, and invoicing party details.
It can mean the same entity is being used throughout the process—but it can also reflect inconsistent data entry or different roles (ordering vs. invoicing vs. dispatch). Look for consistent addresses, legal identifiers, tax IDs, invoice remittance details, and reconciliation fields. If any of these differ, treat it as a potential mapping discrepancy even if the name looks the same.
Ask for a documented returns/RMA procedure, who owns corrective actions, and how lot/serial traceability is maintained. Ensure that responsibility is aligned with the entity that actually issues invoices and receives return items. If the dispatch party is different from the invoice party, confirm who is responsible for quality documentation and corrective action evidence.
Pause new purchasing until the mapping is clarified, or apply controlled purchasing. Controlled purchasing can include requiring additional documentation (legal entity confirmation, address verification, invoice/PO matching fields, dispatch documentation requirements) and confirming returns ownership before shipment. Additionally, consider implementing AP holds so invoices that do not match expected vendor master mappings are paused pending verification.
You should verify. Supplier-provided information is a starting point, but procurement governance typically requires cross-checking documents already in your workflow to ensure traceability and reduce reconciliation risk. Verification should include field-level alignment and consistency checks across the full document chain (RFQ/quote → PO → delivery/receiving → invoice).
No. Contracts define legal responsibility and service terms. This guide focuses on operational interpretation of supplier identifiers so that contracts and transactions align correctly in day-to-day execution. Even with a strong contract, operational mapping errors can cause invoice mismatches, delayed claims, and audit issues—so governance must connect contracts to actual document behavior.
Price and supplier details are part of the purchasing record, but they should be tied to the verified entity mapping. When the identifier (such as Valdemar) is used in quotes or pricing, confirm that the same entity also aligns with invoicing and fulfillment responsibilities. If price is quoted by one entity but invoicing happens under another entity, the procurement record should reflect the contract and financial responsibility correctly.
If fdossantos or another identifier appears to function as a contact alias rather than a legal or operational entity, procurement should clarify the nature of the identifier. Confirm the legal vendor entity for contracting, the invoicing entity for AP, and the dispatch entity for shipping documents. Contact aliases should not be used as the sole basis for vendor master records unless your finance/legal process explicitly supports that mapping.
A practical minimum evidence set includes: (1) legal entity name and verified address matching your vendor master record, (2) PO-to-invoice matchability (invoice issued under a mapped entity), (3) receiving-to-invoice reconciliation alignment, and (4) documented responsibility for returns/quality claims when applicable. For regulated goods or lot/serial traceability needs, add traceability evidence that links lot/serial numbers to the delivered items.
Score based on responsibility and mapped entity roles rather than on raw identifier text. If “Arjemiro” is the dispatch/fulfillment node while the legal entity is different, decide which entity is accountable for dispatch performance in your scorecard structure. For financial performance metrics (invoice match rate, AP rework), use the invoicing entity mapping. This separation prevents misleading performance signals caused by inconsistent identifiers.
In procurement practice, Valdemar, Arjemiro, and fdossantos should be handled as traceable identifiers within a wider workflow—not as assumptions about who a supplier “is.” By validating identity mapping, ensuring document consistency, and establishing clear responsibility boundaries, organizations can reduce operational friction and improve audit readiness. When in doubt, use the step-by-step verification process and apply the stated conditions for proceeding.
Ultimately, the best procurement outcome is not merely “having the right vendor name,” but having the right mapping between names and responsibilities across the end-to-end process. When your team can trace a transaction from PO to receiving to payment—with clear evidence of who owns quality, dispatch, and returns—you turn ambiguous identifiers into reliable, measurable procurement pathways.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
4rkojvsx Technology: Industry Insights and Buying Guide
Affordable Phones and Plans for Seniors
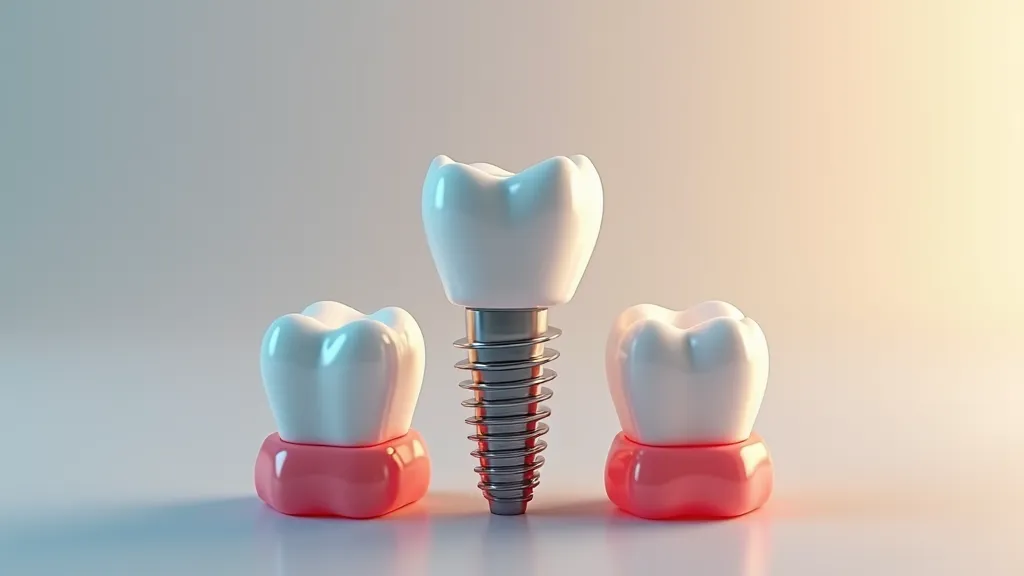
Affordable Full Mouth Dental Implants Near You
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
WLLE: Practical Sourcing Insights with Quality Focus
This guide explains how WLLE helps organize sourcing decisions by balancing specification clarity, supplier reliability, and quality checks. Objectively, “WLLE” is treated here as a practical workflow label, while the repeated “😊 😊 😊” cues a user-experience orientation rather than a technical claim. The article also outlines decision conditions, comparison criteria, and FAQs for buyers.
Pis: Expert Buying Guide and Supplier Comparison
This guide explains Pis in an objective, decision-ready way—covering typical supplier considerations, evaluation criteria, and practical steps to choose what fits your needs. The background sections clarify what “Pis” generally refers to in commerce contexts, common use cases, and why supplier transparency matters when you compare options.
Revisional Porto Alegre: Expert Guidance and Options
This guide explains how a revisional approach is applied in Porto Alegre, outlining practical steps, due diligence, and supplier selection considerations. “Revisional Porto Alegre” refers to reviewing, adjusting, and verifying prior arrangements or plans to reduce risk and improve outcomes. The article offers an objective industry lens and a structured checklist for requirements, sources, and common questions.
Understanding Cxxxvldlo Supply Quality Standards
This guide explains how Cxxxvldlo-related supply quality is evaluated, organized, and verified across sourcing workflows. Objectively, it frames what “Cxxxvldlo” typically represents in operational contexts, why documentation and auditability matter, and how procurement teams translate supplier requirements into consistent handling. The goal is clarity—so decisions remain traceable, repeatable, and compliant.
Pono Explained: Meaning, Use, and Buyer Guidance
This guide clarifies what Pono is, how it’s commonly used, and how to evaluate quality when sourcing it for personal or commercial purposes. It objectively outlines the background of Pono terminology, common product forms, typical supplier roles, and practical decision criteria—so you can compare options confidently without relying on vague claims.
Understanding Joao.clemente.de.soiza.c.p.f Identifiers
This guide explains how to interpret the identifier “Joao.clemente.de.soiza.c.p.f” in real-world record workflows and compliance contexts. It then provides objective background on what such code-like strings typically represent, how organizations verify them, and what quality controls reduce errors. The discussion focuses on responsible handling, traceability, and audit readiness without relying on unverified claims.